Case study 04 / Australian Pharmacist CPD / 2026
From AI prototype to production
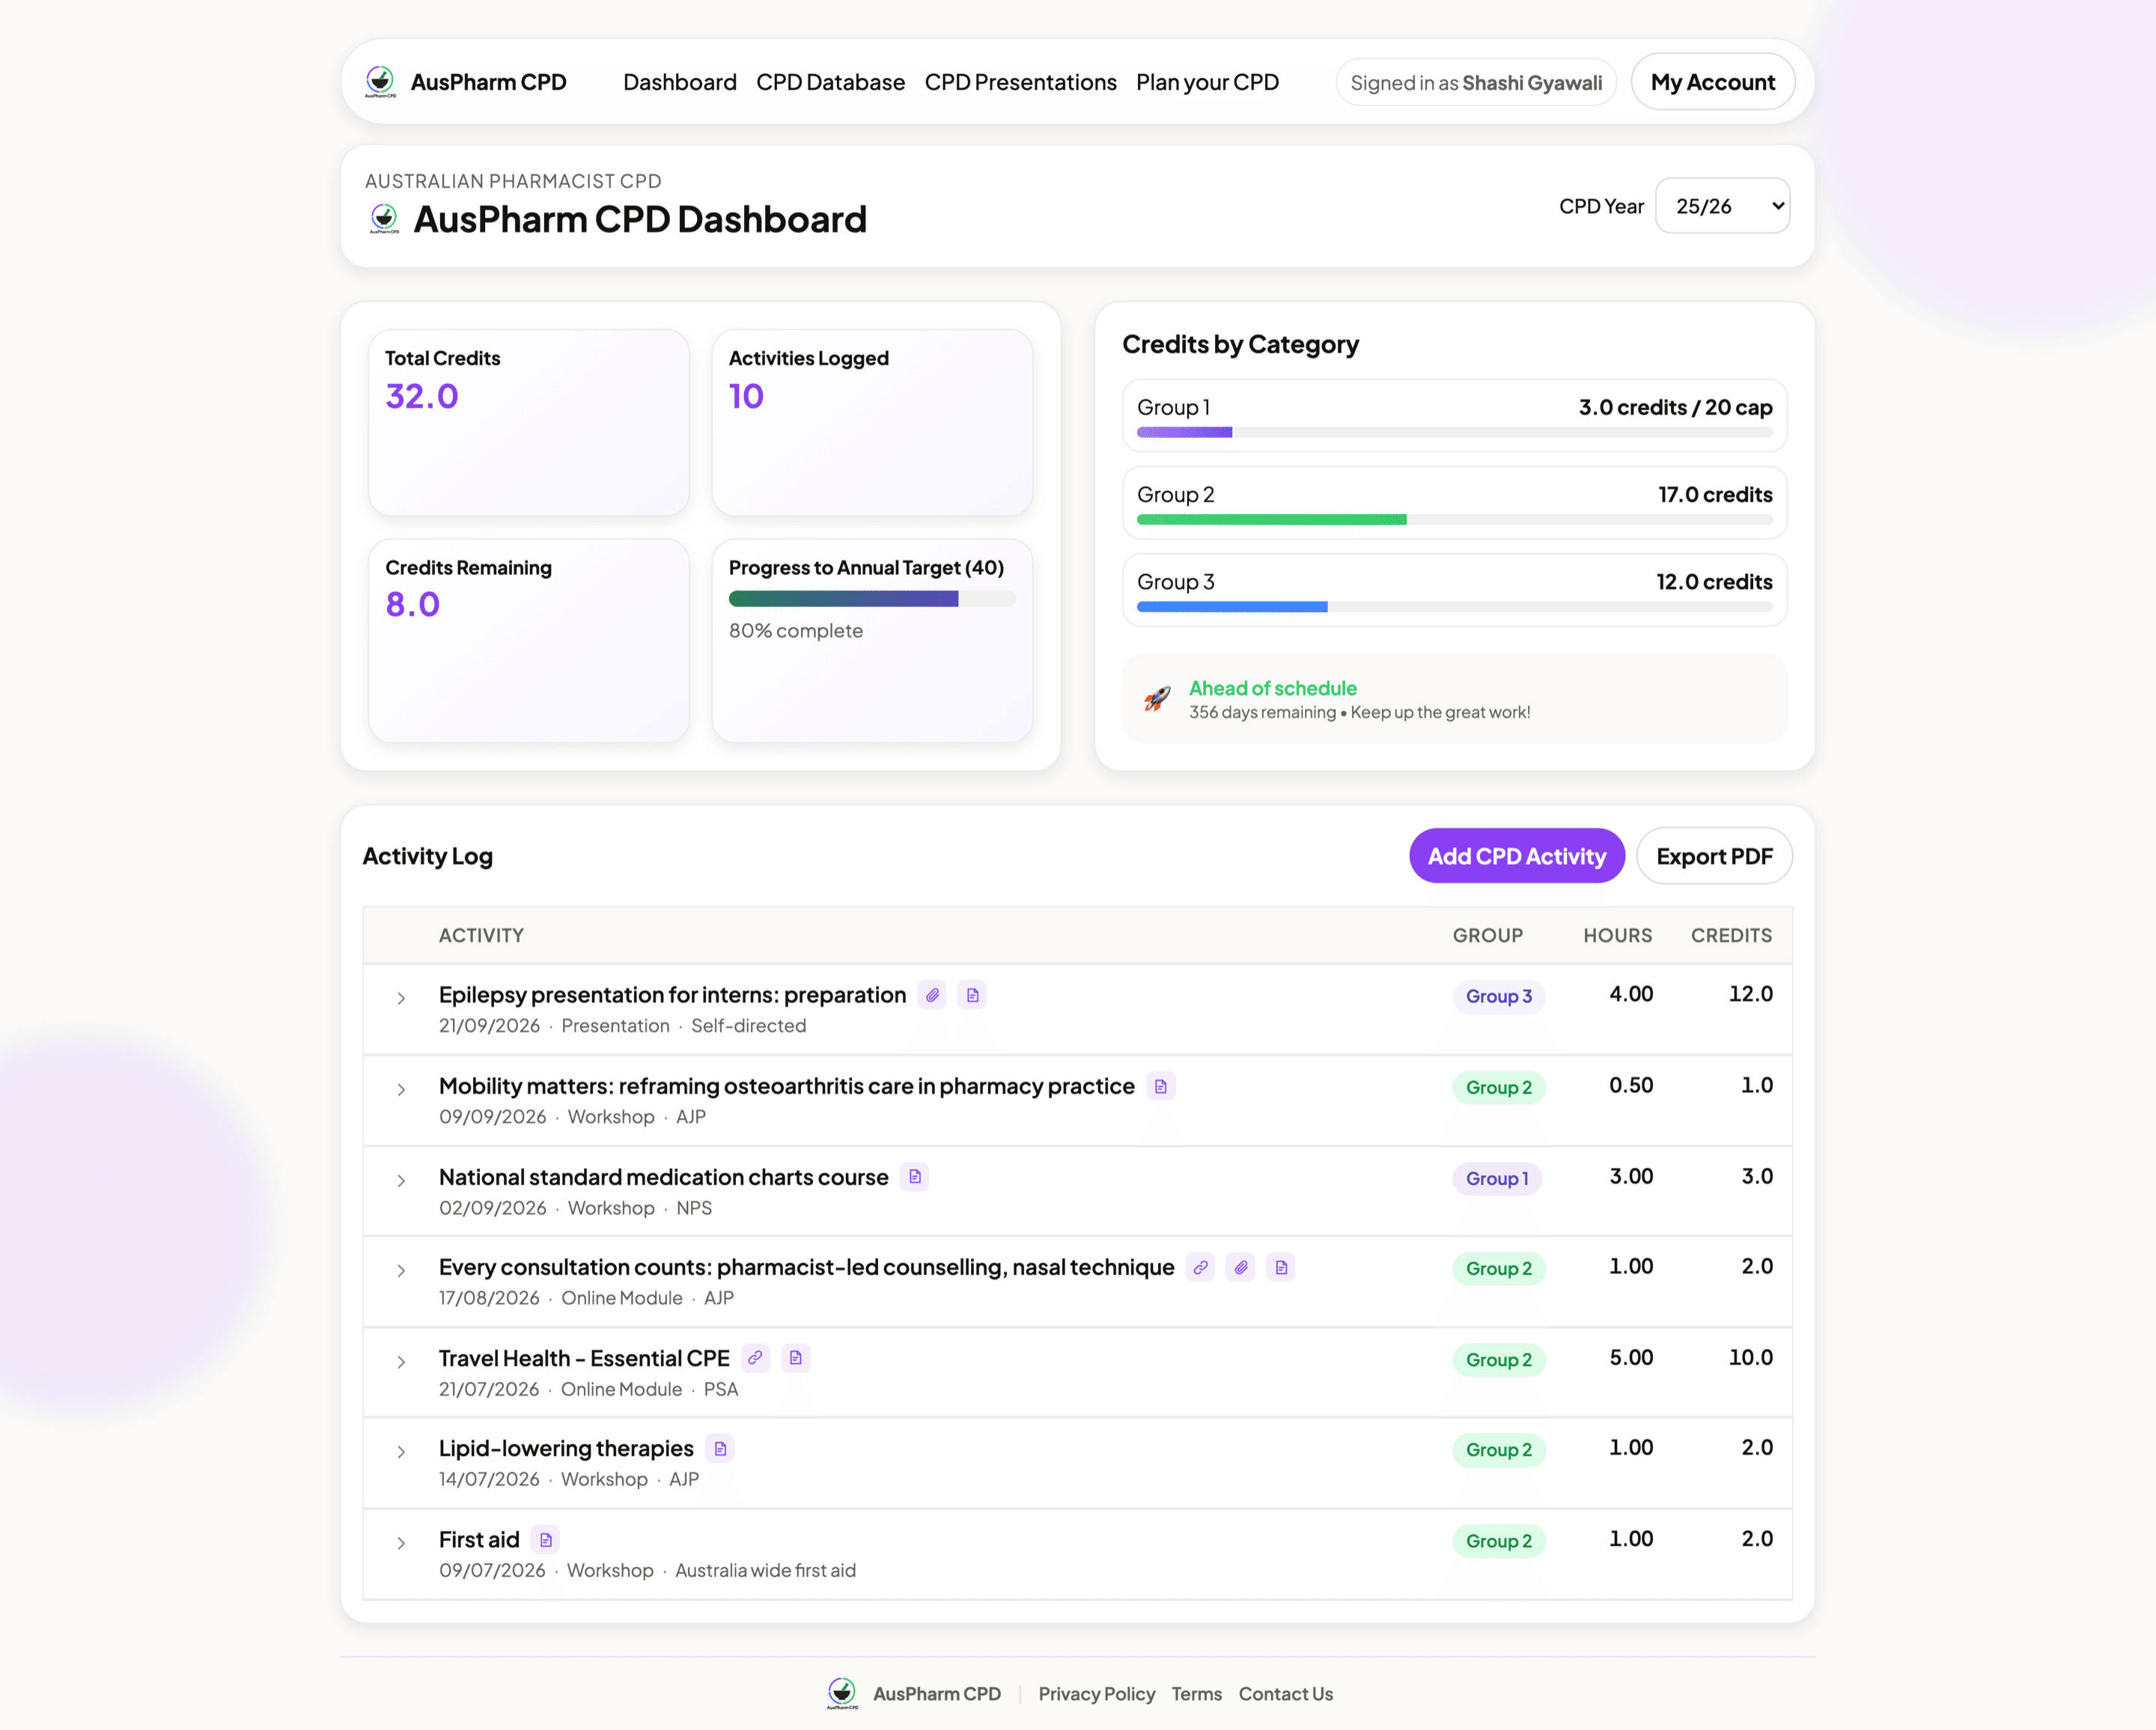
A continuing-professional-development platform Australian pharmacists use to record and report their CPD. A non-technical founder had built roughly 80% of it with AI coding tools. I came in as the only engineer and made it safe to run.
Result
Sole full-stack engineer
2026 – present
JavaScript, Firebase, Cloud Functions, Firestore, Stripe
Architecture, security, payments, privacy
The problem
AI tools got the founder a working demo fast. They also produced a 4,700-line JavaScript file, client-side trust, and no real answer for payments, regulated personal data, or someone gaming the free trial. It looked finished and was nowhere near shippable.
Architecture
- I built
- Managed service
- Region boundary
- 01Matches a build point
What I built
Decomposed the monolith into 40+ ES2022 front-end modules and around 20 Cloud Functions, governed by a one-directional dependency rule so it stays that way.
Moved trust to the server: admin rights, subscriptions, payments and audit logs enforced through Firebase custom claims, Cloud Functions and field-level Firestore rules, not the browser.
Hardened sign-in with a two-step custom-token flow, progressive brute-force lockout, App Check (ReCaptcha v3), and recent-auth gating on destructive actions.
A full Stripe subscription system (embedded checkout, free trials, billing portal) on idempotent signature-verified webhooks, with a trial-conversion fraud guard.
Privacy and data lifecycle for a regulated domain: recursive account deletion with certificate cleanup, and Cloud Functions region-pinned for Australian data residency.
Modelled the CPD regulatory rules as pure, unit-tested functions behind a regression suite, with Playwright E2E cover on the auth flows.